Critical UEFI Firmware Flaw Exposes Network-Booting Servers to Attack
A memory-corruption bug in EDK II, the open-source base of most server firmware, could let attackers run code before Secure Boot starts.
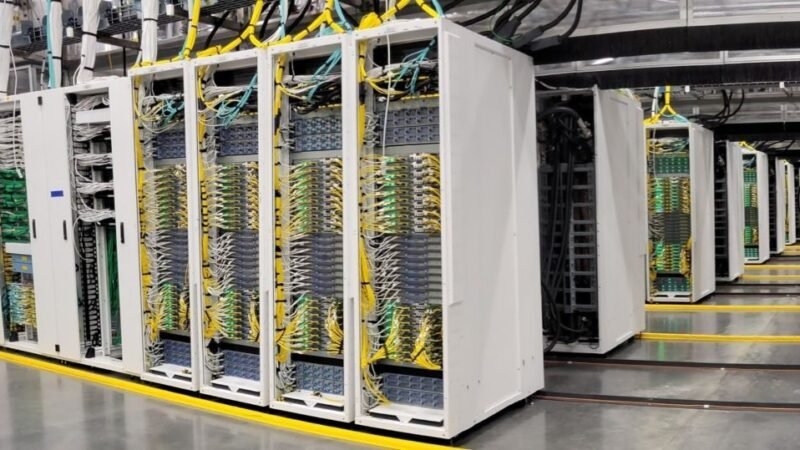
A serious security flaw in the open-source code used to build the startup firmware of most of the world’s servers could let attackers run malicious code before the operating system, and its built-in defenses, even begin to load, Ars Technica reported on Tuesday. The bug, tracked as CVE-2026-97631, sits in TianoCore EDK II, a widely shared codebase for UEFI firmware, the low-level software that starts a computer and hands control to its operating system.
What happened
According to Ars Technica, the vulnerability is a memory-corruption flaw in a part of EDK II that handles ICMP, the Internet Control Message Protocol that networked machines use to exchange error and status messages. Amazon Web Services, in its public security advisory for the issue, describes it as an out-of-bounds write and classic buffer overflow caused by an incorrect buffer size calculation. Amazon said a successful attack can lead to arbitrary code execution, with a high impact on the confidentiality, integrity and availability of an affected system.
The sources differ on how severe the flaw is. Ars Technica reported a severity rating of 9.5 out of 10. Amazon’s advisory, which was published on Oct. 22, lists a score of 8.3 under the CVSS 3.1 scoring system and classifies the bug as “Important.” Amazon’s scoring indicates that an attacker would need access to an adjacent network, such as the same local network, and that the attack is relatively complex to pull off, though it requires no login and no action by a user.
The flaw was found by Alex Matrosov, a firmware security researcher at Anthropic, and Dan Holmes of Google, according to Ars Technica. The researchers had planned a coordinated disclosure, a process in which details are kept private until fixes are ready, for January. That timeline fell apart after AMI, one of the largest firmware suppliers, published a public code change that described the bug and included a fix. TianoCore then released a public advisory.
Why it matters
EDK II is the reference code that much of the firmware industry builds on. Ars Technica reported that virtually all major UEFI suppliers, including AMI, Insyde and Phoenix, rely heavily on it, and that Project Mu, Microsoft’s hardened version of the codebase, also contained the affected component. That reach is why the outlet described the bug as a threat to most servers on the planet.
The timing of the attack is what makes firmware flaws especially worrying to security teams. Because the malicious code would run so early in startup, it would execute before protections such as Secure Boot, which checks that only trusted software loads, and the TPM, a security chip that stores encryption keys and verifies system integrity, are active. Ars Technica reported that the attack payloads do not survive a restart on their own, but they could give attackers an opening to install other code that runs early in the boot process every time a machine starts.
The real-world exposure is narrower than the headline reach suggests. The risk centers on machines that boot over a network, commonly through PXE, a standard that lets servers load their operating systems from a central server rather than a local drive. That setup is common in data centers but rare in homes and small offices, and readers discussing the report on the technology site Slashdot noted that an attacker would generally need a foothold on the same local network to send the crafted messages during startup.
Vendor responses
Several companies have begun to say whether their products are affected, according to reports on the disclosure:
- Intel said none of its commercial products that are still under security support are known to be affected.
- Arm said the flaw does not directly apply to its product portfolio, even though its firmware draws heavily on EDK II.
- Amazon lists a fix as pending for the EDK II package in Amazon Linux 2 and says Amazon Linux 2023 and the Amazon Linux 2027 preview are not affected.
What comes next
Because the fix is now public, Ars Technica warned that skilled attackers could study the patch to work out how to trigger the bug, shrinking the window defenders have to respond. That is a familiar problem with firmware: unlike ordinary apps, UEFI updates usually have to pass from the open-source project to firmware suppliers, then to server and hardware makers, and finally to the companies that run the machines. Ars Technica noted that patching firmware across millions of devices is slow and difficult.
The episode adds to a string of EDK II networking flaws disclosed in recent years, including a group of bugs in its network-boot code that researchers revealed in early 2024. Server makers have not yet published a full list of affected models, and organizations that rely on network booting are likely to watch closely for firmware updates from their hardware vendors in the coming weeks.